SECURITY // DAILY THREAT INTEL
Cyber Threat Intel — September 22, 2026
A compact daily recap of the threats, breaches and exploitation activity worth paying attention to.
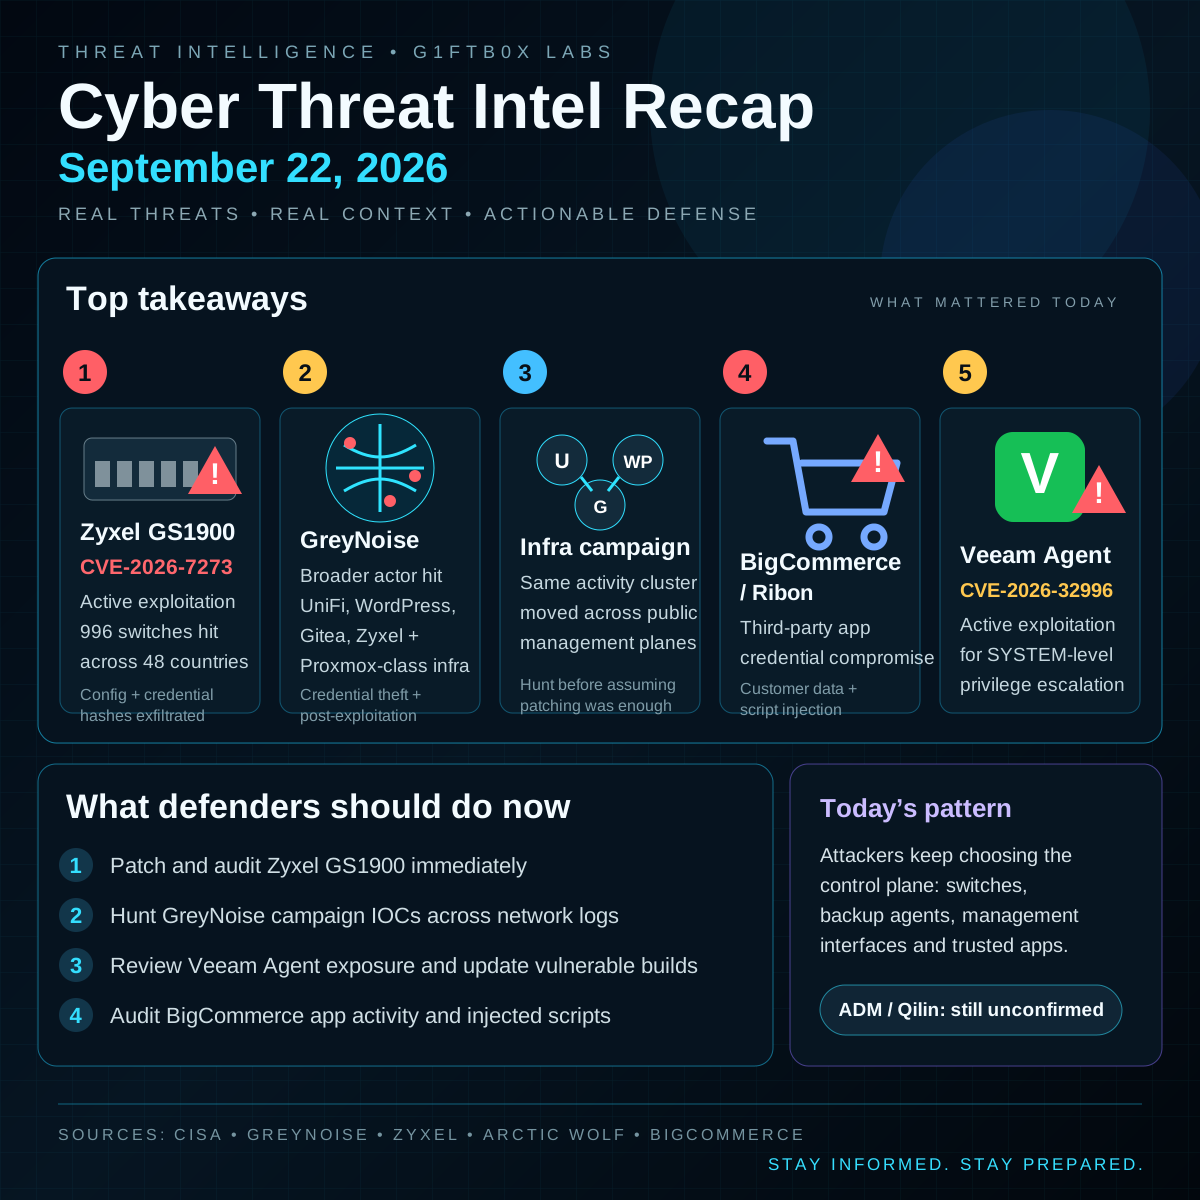
Top developments
- Zyxel GS1900 / CVE-2026-7273: active exploitation moved into CISA KEV. GreyNoise reported 996 switches compromised across 48 countries, with configuration data and hashed credentials taken.
- Broader infrastructure campaign: the same or closely related activity has targeted public management surfaces including UniFi, WordPress, Gitea, Zyxel and Proxmox-class infrastructure.
- BigCommerce / Ribon: a third-party application credential compromise led to customer-data exposure and malicious script injection on affected merchant storefronts.
- Veeam Agent / CVE-2026-32996: exploitation is being observed for SYSTEM-level privilege escalation on vulnerable Windows endpoints.
- Control-plane targeting: management interfaces, backup tooling, network devices and trusted SaaS integrations continue to offer attackers more leverage than a single endpoint.
Source set
This recap was built from current vendor, government and threat-intelligence reporting, including CISA, GreyNoise, Zyxel, Arctic Wolf and BigCommerce. Ransomware leak-site claims are kept separate from confirmed victim disclosures.